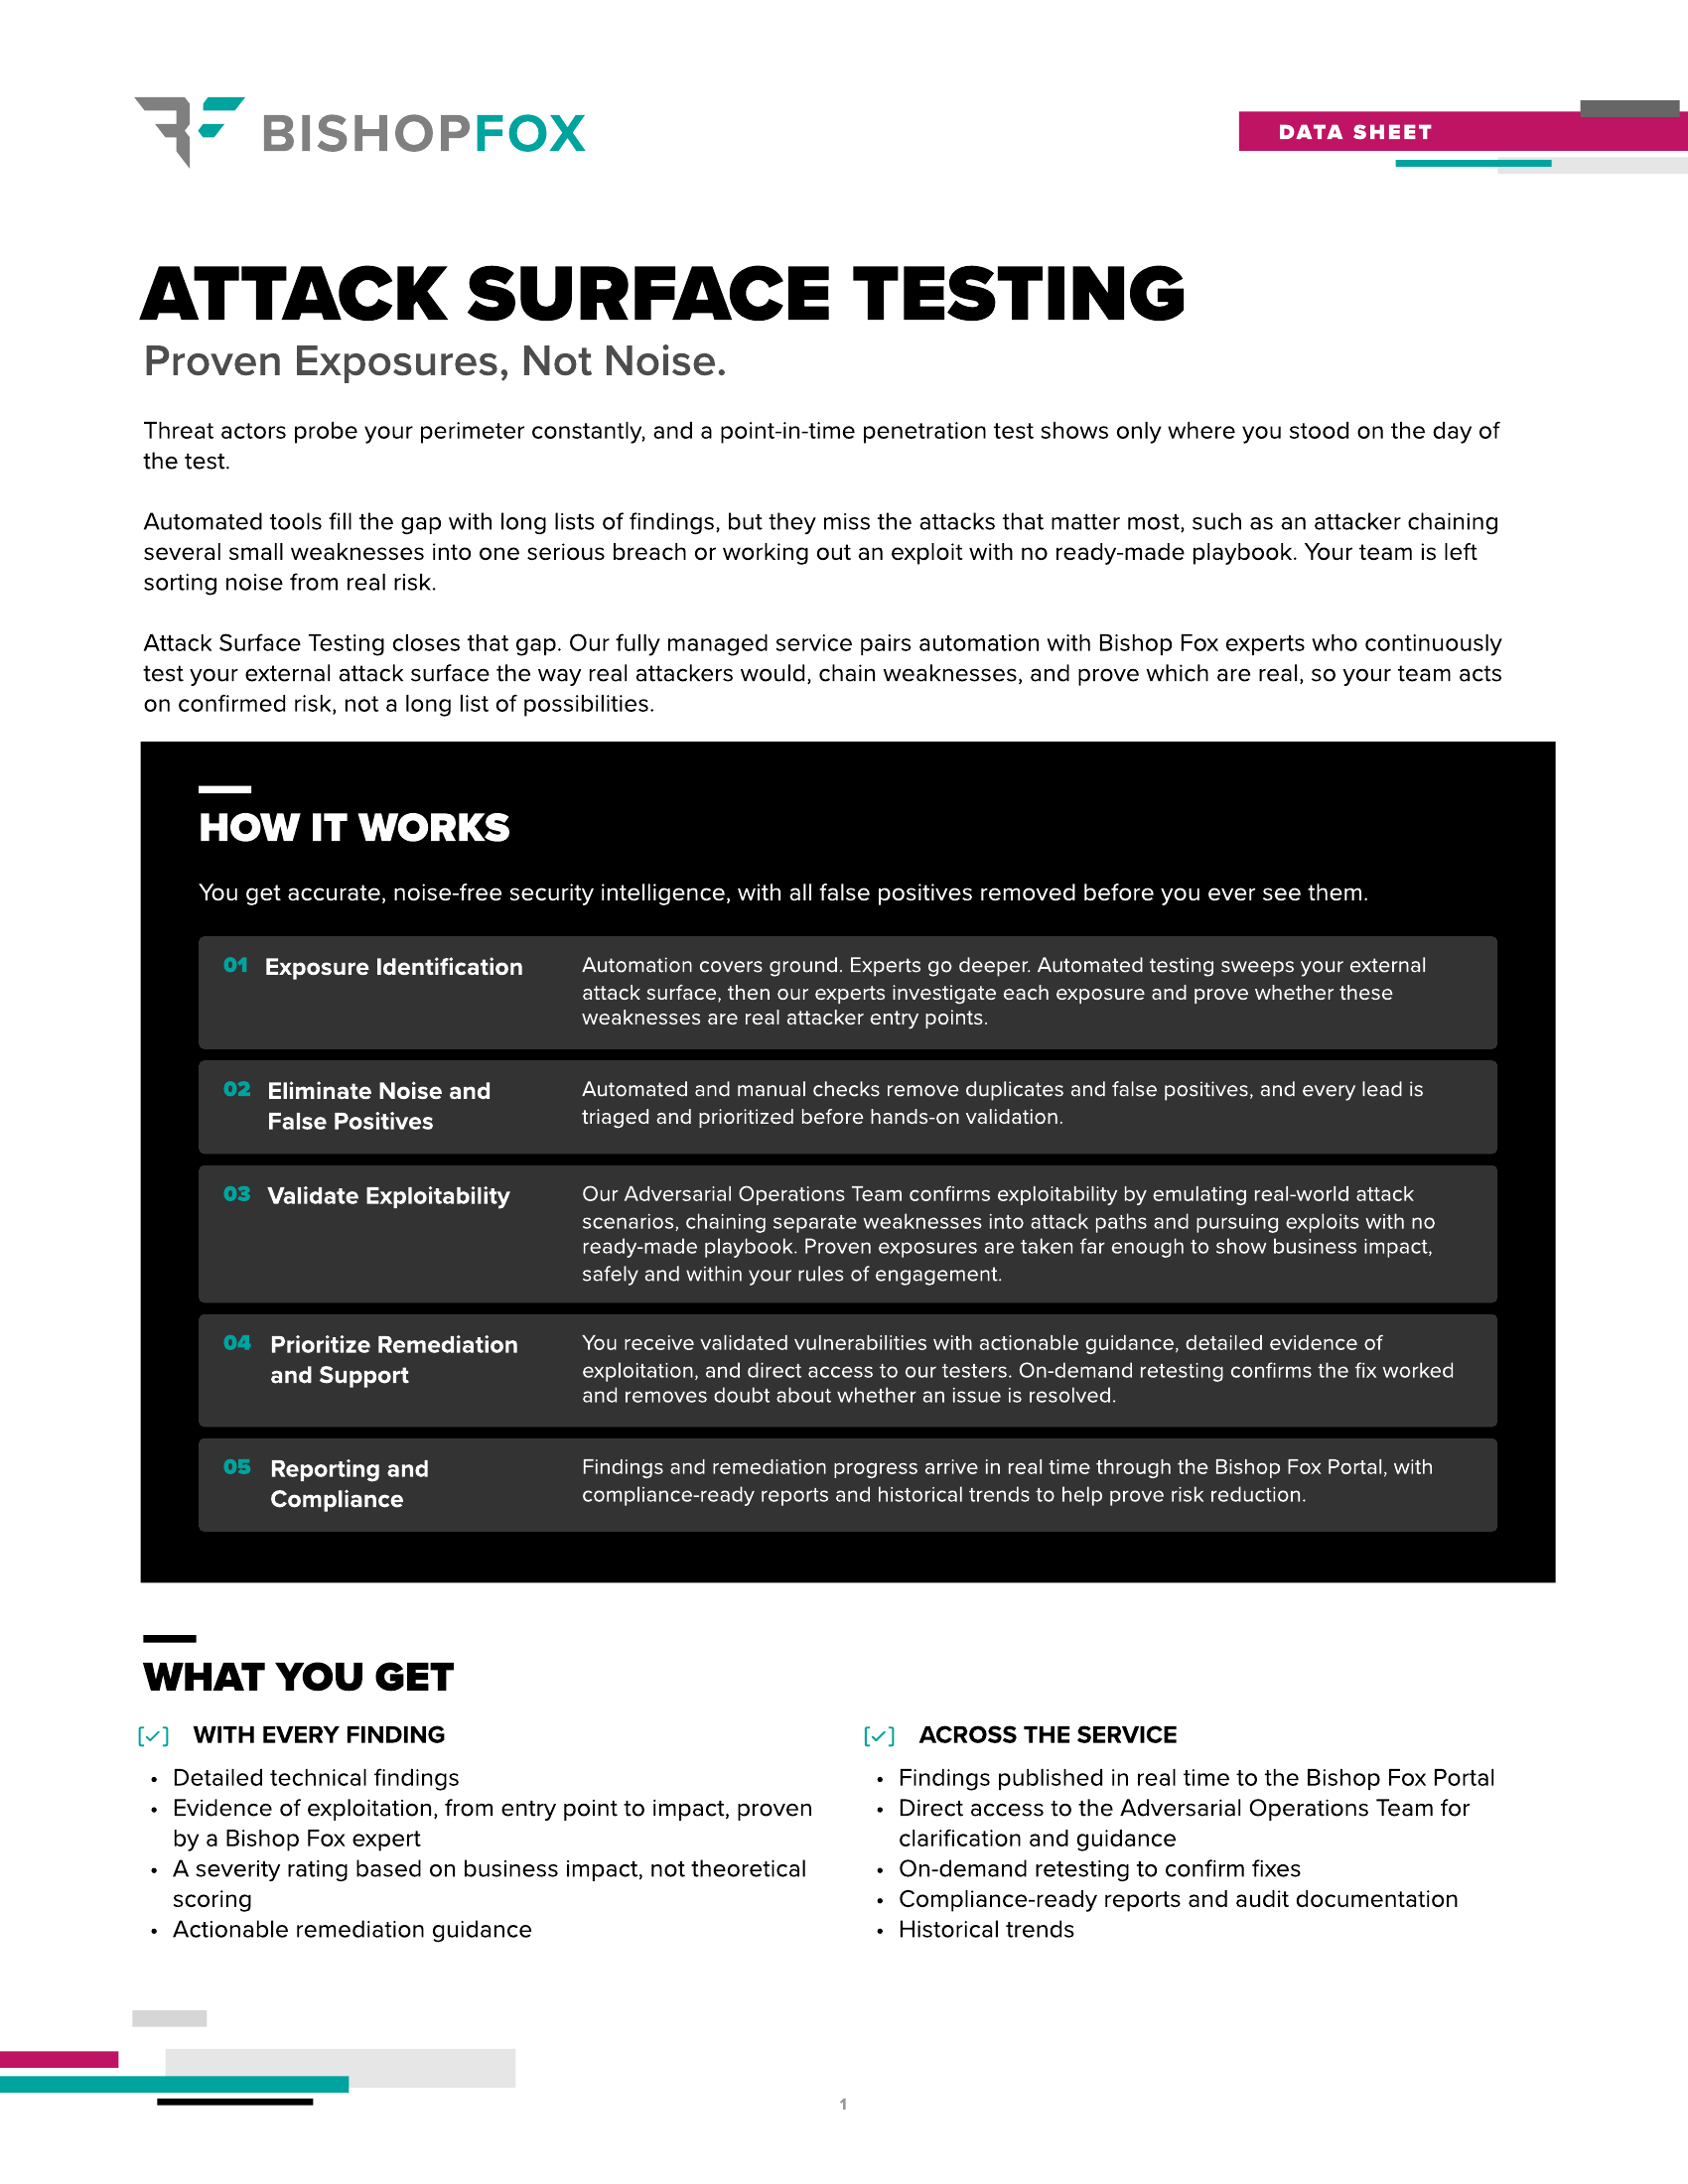
Automated tools fill the gaps between tests with long lists of findings, but they miss the attacks that matter most, such as an attacker chaining several small weaknesses into one serious breach or working out an exploit with no ready-made playbook. Our Attack Surface Testing closes that gap. This fully managed service pairs automation with Bishop Fox experts who continuously test your external attack surface the way real attackers would, chain weaknesses into attack paths, and prove which ones are real. AI-specific vulnerability checks also run against the model servers, LLM endpoints, and MCP services found in your inventory.
Read our datasheet to explore our five-step process, from exposure identification to compliance-ready reporting, and learn how validated findings open in Jira and ServiceNow while status flows back to the Bishop Fox Portal. You will also see how Attack Surface Testing fits into Continuous Security Testing alongside Attack Surface Discovery and Emerging Threat Testing.