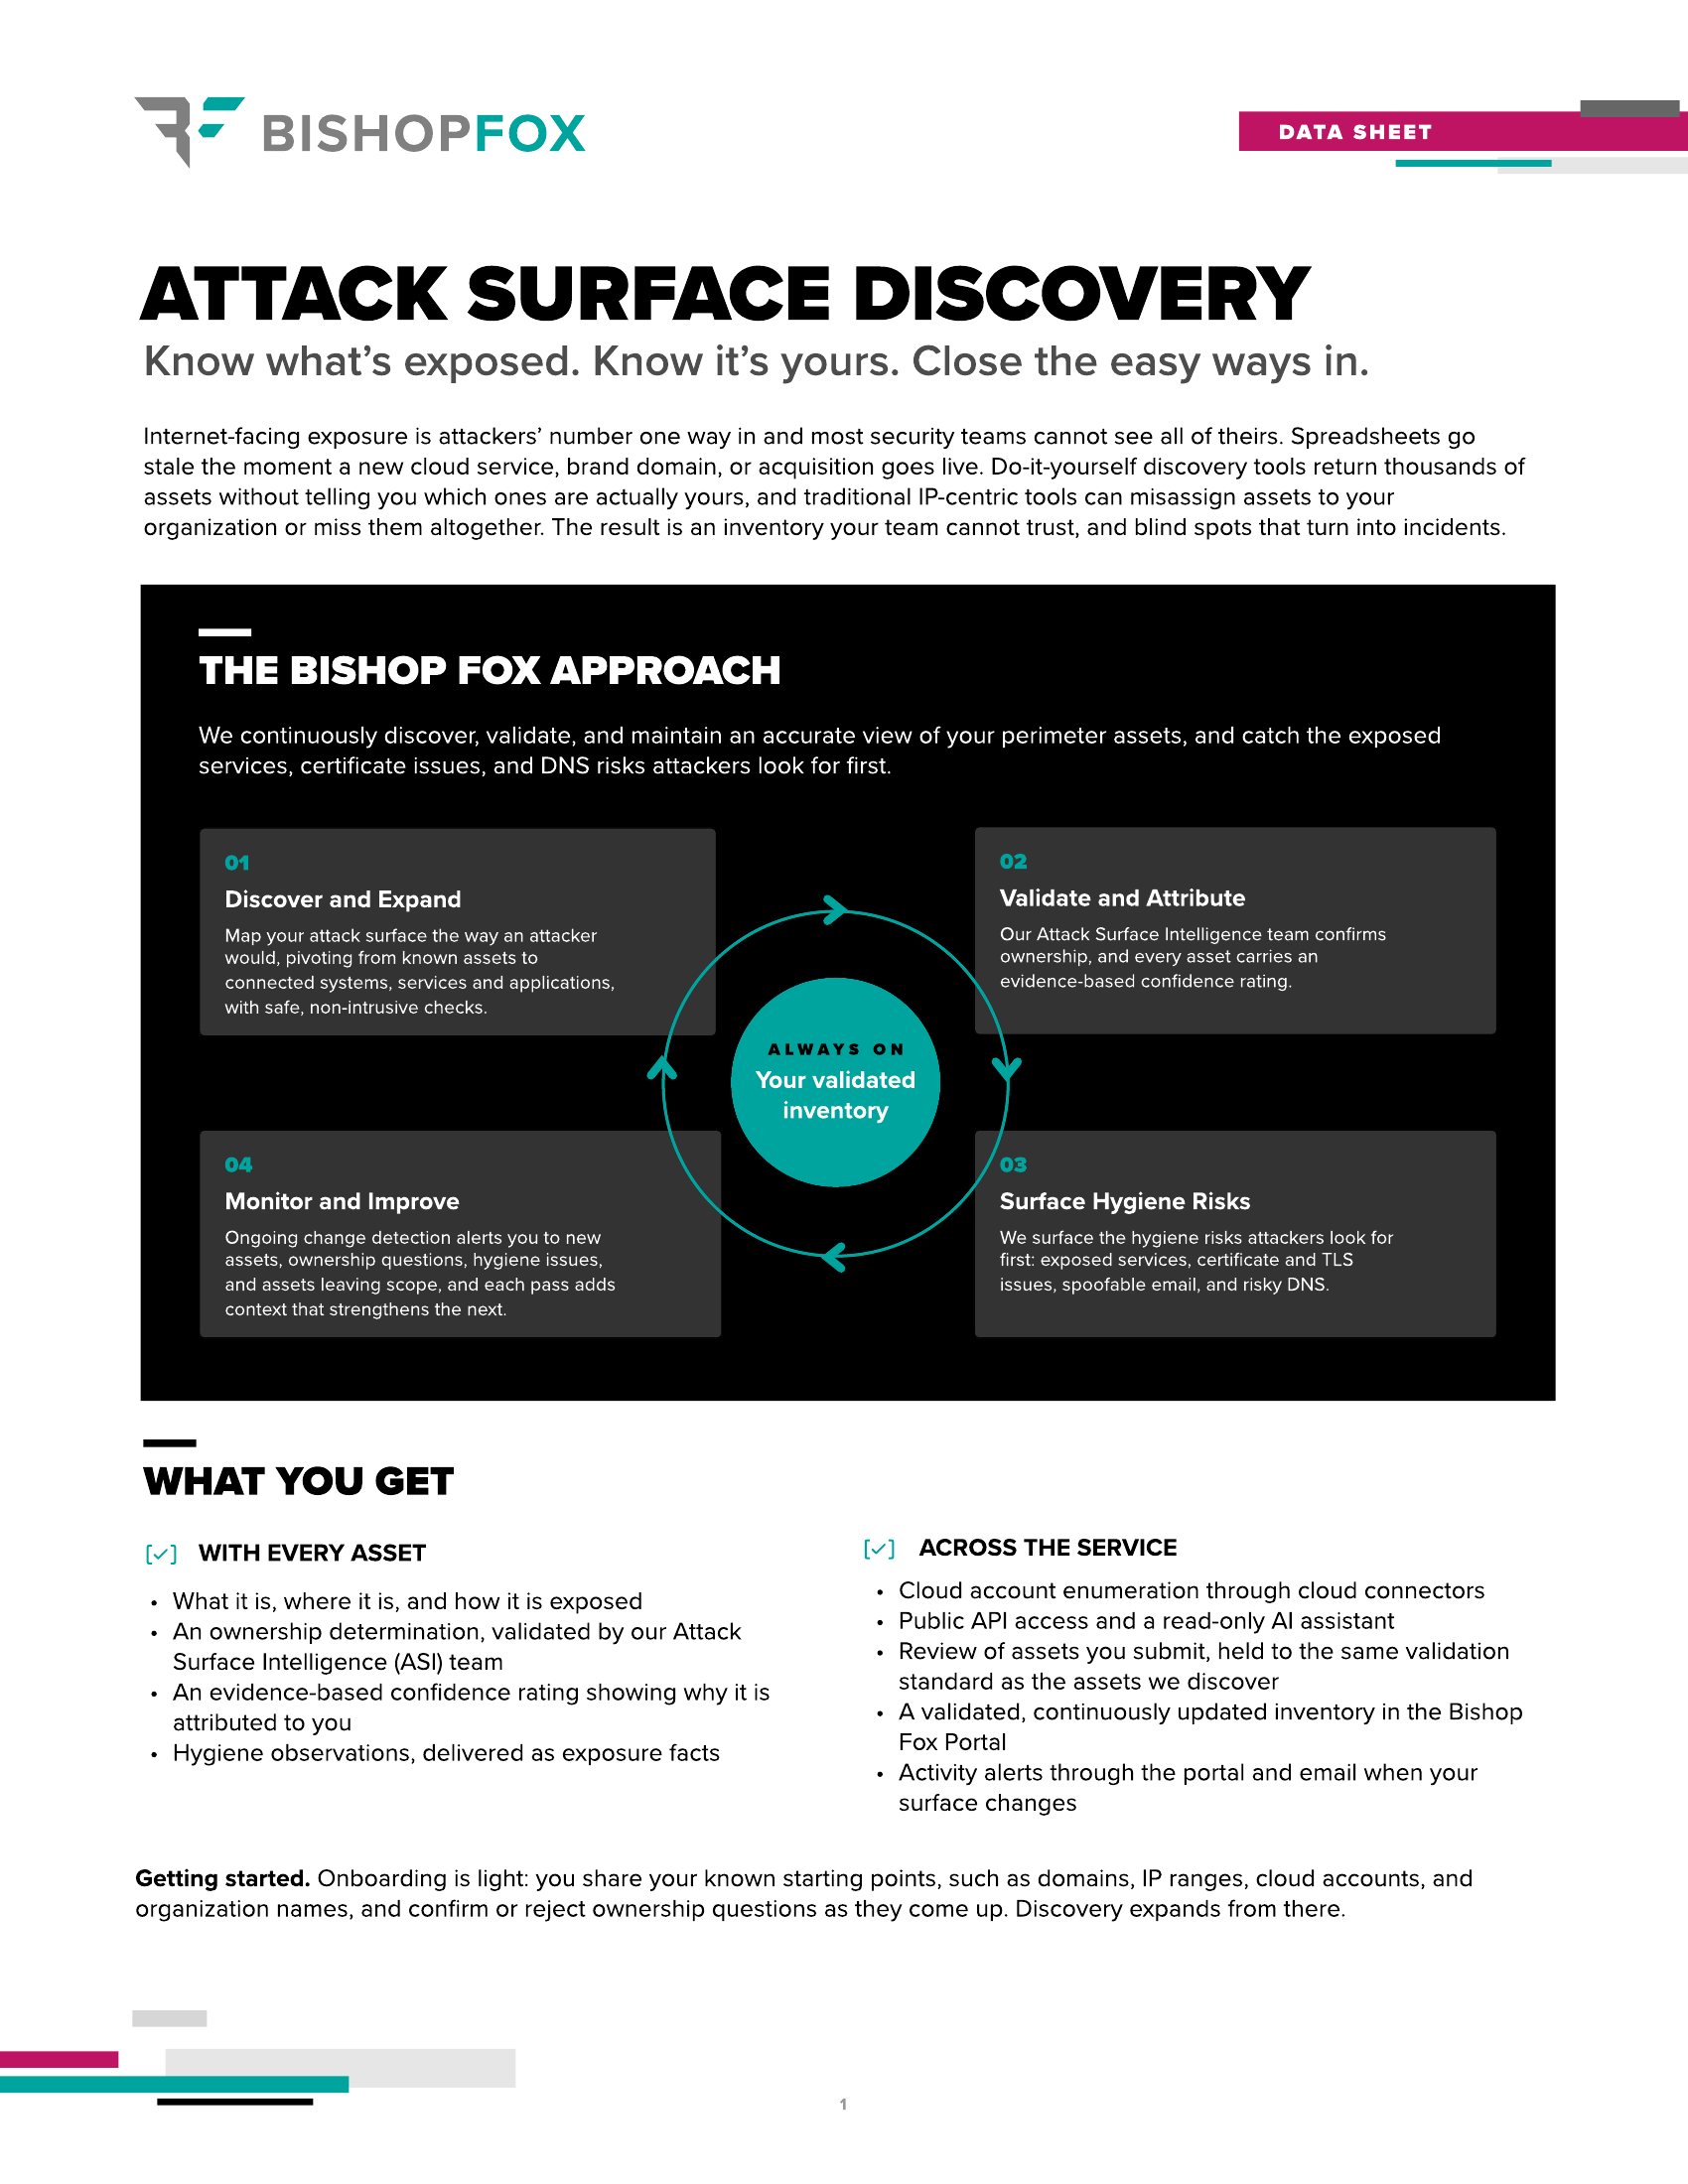
Spreadsheets go stale the moment a new cloud service, brand domain, or acquisition goes live. DIY discovery tools return thousands of assets without telling you which ones are yours, and IP-centric tools can misassign assets or miss them altogether. Our Attack Surface Discovery closes that gap by mapping your attack surface the way an attacker would, then having our Attack Surface Intelligence team confirm ownership so every asset carries an evidence-based confidence rating. Continuous hygiene checks surface the exposed services, certificate and TLS issues, spoofable email, and risky DNS that attackers look for first.
Read our datasheet to explore our four-step approach, from discovery and attribution to hygiene risks and ongoing change detection, and see how your validated inventory connects to Jira, ServiceNow, and the public API. You will also learn how Attack Surface Discovery gives the rest of our Continuous Security Testing offerings a live, validated scope to work from.