CONTINUOUS SECURITY TESTING
Testing That Never Stops. Proof That Never Wavers.
Attackers don't wait for your next scheduled test. Neither should you. Bishop Fox Continuous Security Testing (CST) shows you what's exposed on your attack surface, proves what's exploitable, and tells you how the latest threats impact your environment, with our experts standing behind every result.
d88P Y88b d8888
888 888 888
888 888 888
888 888 888
888 888 888
Y88b d88P 888
"Y8888P" 8888888
BEYOND THE SNAPSHOT
GET MORE COVERAGE, WITH LESS WORK FOR YOUR TEAM
A scheduled test is a snapshot. The moment it ends, your attack surface changes and new threats arrive. Keeping up means maintaining a perimeter view you can trust, separating real exposures from noise, and checking every new threat against your environment. Bishop Fox does that work for you. We keep your view current, prove what is exploitable, and tell you whether new threats put you at risk, all managed by experts who stand behind every result.
A Managed Service, Not Another Tool
Bishop Fox investigates, prioritizes, and confirms results, then delivers detailed evidence, clear remediation guidance, and direct access to our testers, so your team can act quickly.
Results You Can Trust
From asset ownership to exploitation to emerging threats, every result is confirmed by Bishop Fox and prioritized for you, so your team spends its time only on what is real.
Always-On Coverage
Coverage runs continuously, so new assets, new exposures, and new threats surface as they appear, not at your next scheduled test. Your view of risk stays current as your attack surface changes.
Flexible by Design
No two security programs are alike. Our services are built to work together, yet each stands alone, so you can start where your need is greatest and add coverage as your program grows.
d88P Y88b d88P Y88b
888 888 888
888 888 .d88P
888 888 .od888P"
888 888 d88P"
Y88b d88P 888"
"Y8888P" 888888888
Delivered as a managed service, Flexible by Design to adapt as your needs change.
From Pressing Questions to Proven Answers
Attack Surface Discovery
What am I exposing, is it really mine, what are the easy ways in?
- Continuous discovery of perimeter assets
- Validation with confidence ratings
- Hygiene issues that attackers look for first
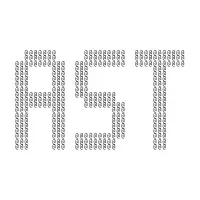
Attack Surface Testing
What exposures can an attacker actually exploit?
- Exploitation across your perimeter
- Depth a scanner can't reach
- Expert-proven findings with evidence
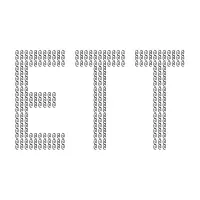
Emerging Threat Testing
Does this new threat affect me, am I in the clear?
- Clear verdicts for your environment
- Original research, in-house checks
- Fixes confirmed after you patch
d88P Y88b d88P Y88b
888 888 .d88P
888 888 8888"
888 888 "Y8b.
888 888 888 888
Y88b d88P Y88b d88P
"Y8888P" "Y8888P"
Build the program that fits your priorities.
What each service provides
How CST Fits Your Exposure Management Program
Continuous Threat Exposure Management (CTEM) is Gartner's framework for continuously managing exposure. CST is how Bishop Fox delivers against it: Attack Surface Discovery, Attack Surface Testing, and Emerging Threat Testing support the cycle, always on and managed by experts. See how Bishop Fox supports a CTEM program.
Get Clarity Without The Complexity
Every CST service is delivered through the Bishop Fox Portal, so results, activity, and history live in one place instead of scattered across tools and reports.
- One validated view. Everything lands in one portal, segmented and access-controlled by user and team, and it stays live between engagements, not just when a report arrives.
- Fits your workflow. Findings flow into Jira and ServiceNow, data pulls through the public API, and a read-only AI assistant answers questions about your results, so CST works with the tools your team already uses.
- The experts behind every result. The Bishop Fox team that did the work is reachable for context and questions.
| Capability | ASD | AST | ETT |
|---|---|---|---|
| Continuous discovery of internet-facing assets | |||
| Ownership validation with an evidence-based confidence rating | |||
| Hygiene findings (certificate and TLS, DNS, email, exposed services) | |||
| Proof of exploitability, captured as evidence | |||
| Emerging threat notification | |||
| Impact determination on newly disclosed vulnerability | |||
| Expert retesting to confirm your fixes worked | |||
| Bishop Fox Portal access |
d88P Y88b d8P888
888 888 d8P 888
888 888 d8P 888
888 888 d88 888
888 888 8888888888
Y88b d88P 888
"Y8888P" 888




d88P Y88b 888
888 888 888
888 888 8888888b.
888 888 "Y88b
888 888 888
Y88b d88P Y88b d88P
"Y8888P" "Y8888P"
Frequently Asked Questions
What is Continuous Security Testing?
Continuous Security Testing (CST) is Bishop Fox’s family of managed services for always-on testing of your attack surface. It includes Attack Surface Discovery, Attack Surface Testing, and Emerging Threat Testing, which work together or independently.
Do I need all three services?
No. The services are modular, so you can start with any one and add others at any time. Many teams pair them, but each delivers value on its own.
How do I see my results?
Every result lands in the Bishop Fox Portal, with a public API and a read-only AI assistant. The Bishop Fox experts behind each result are available for questions.
How is continuous security testing different from an annual penetration test?
A penetration test shows where you stood on the day of the test. Continuous Security Testing keeps discovery, expert testing, and emerging threat checks running as your environment changes, so new assets, exposures, and threats surface as they appear.
How does CST relate to CTEM?
CTEM is Gartner’s program framework for continuously managing threat exposure. CST is how Bishop Fox delivers against that cycle: always on, validated, and managed rather than assessed once a year.

Ready to Get Started?
Let's Connect.
Investing in Continuous Security Testing? We'd love to discuss how we can help you on your journey.