Are your security controls actually stopping attacks—or just generating alerts?
Put Your Security Controls To The Test
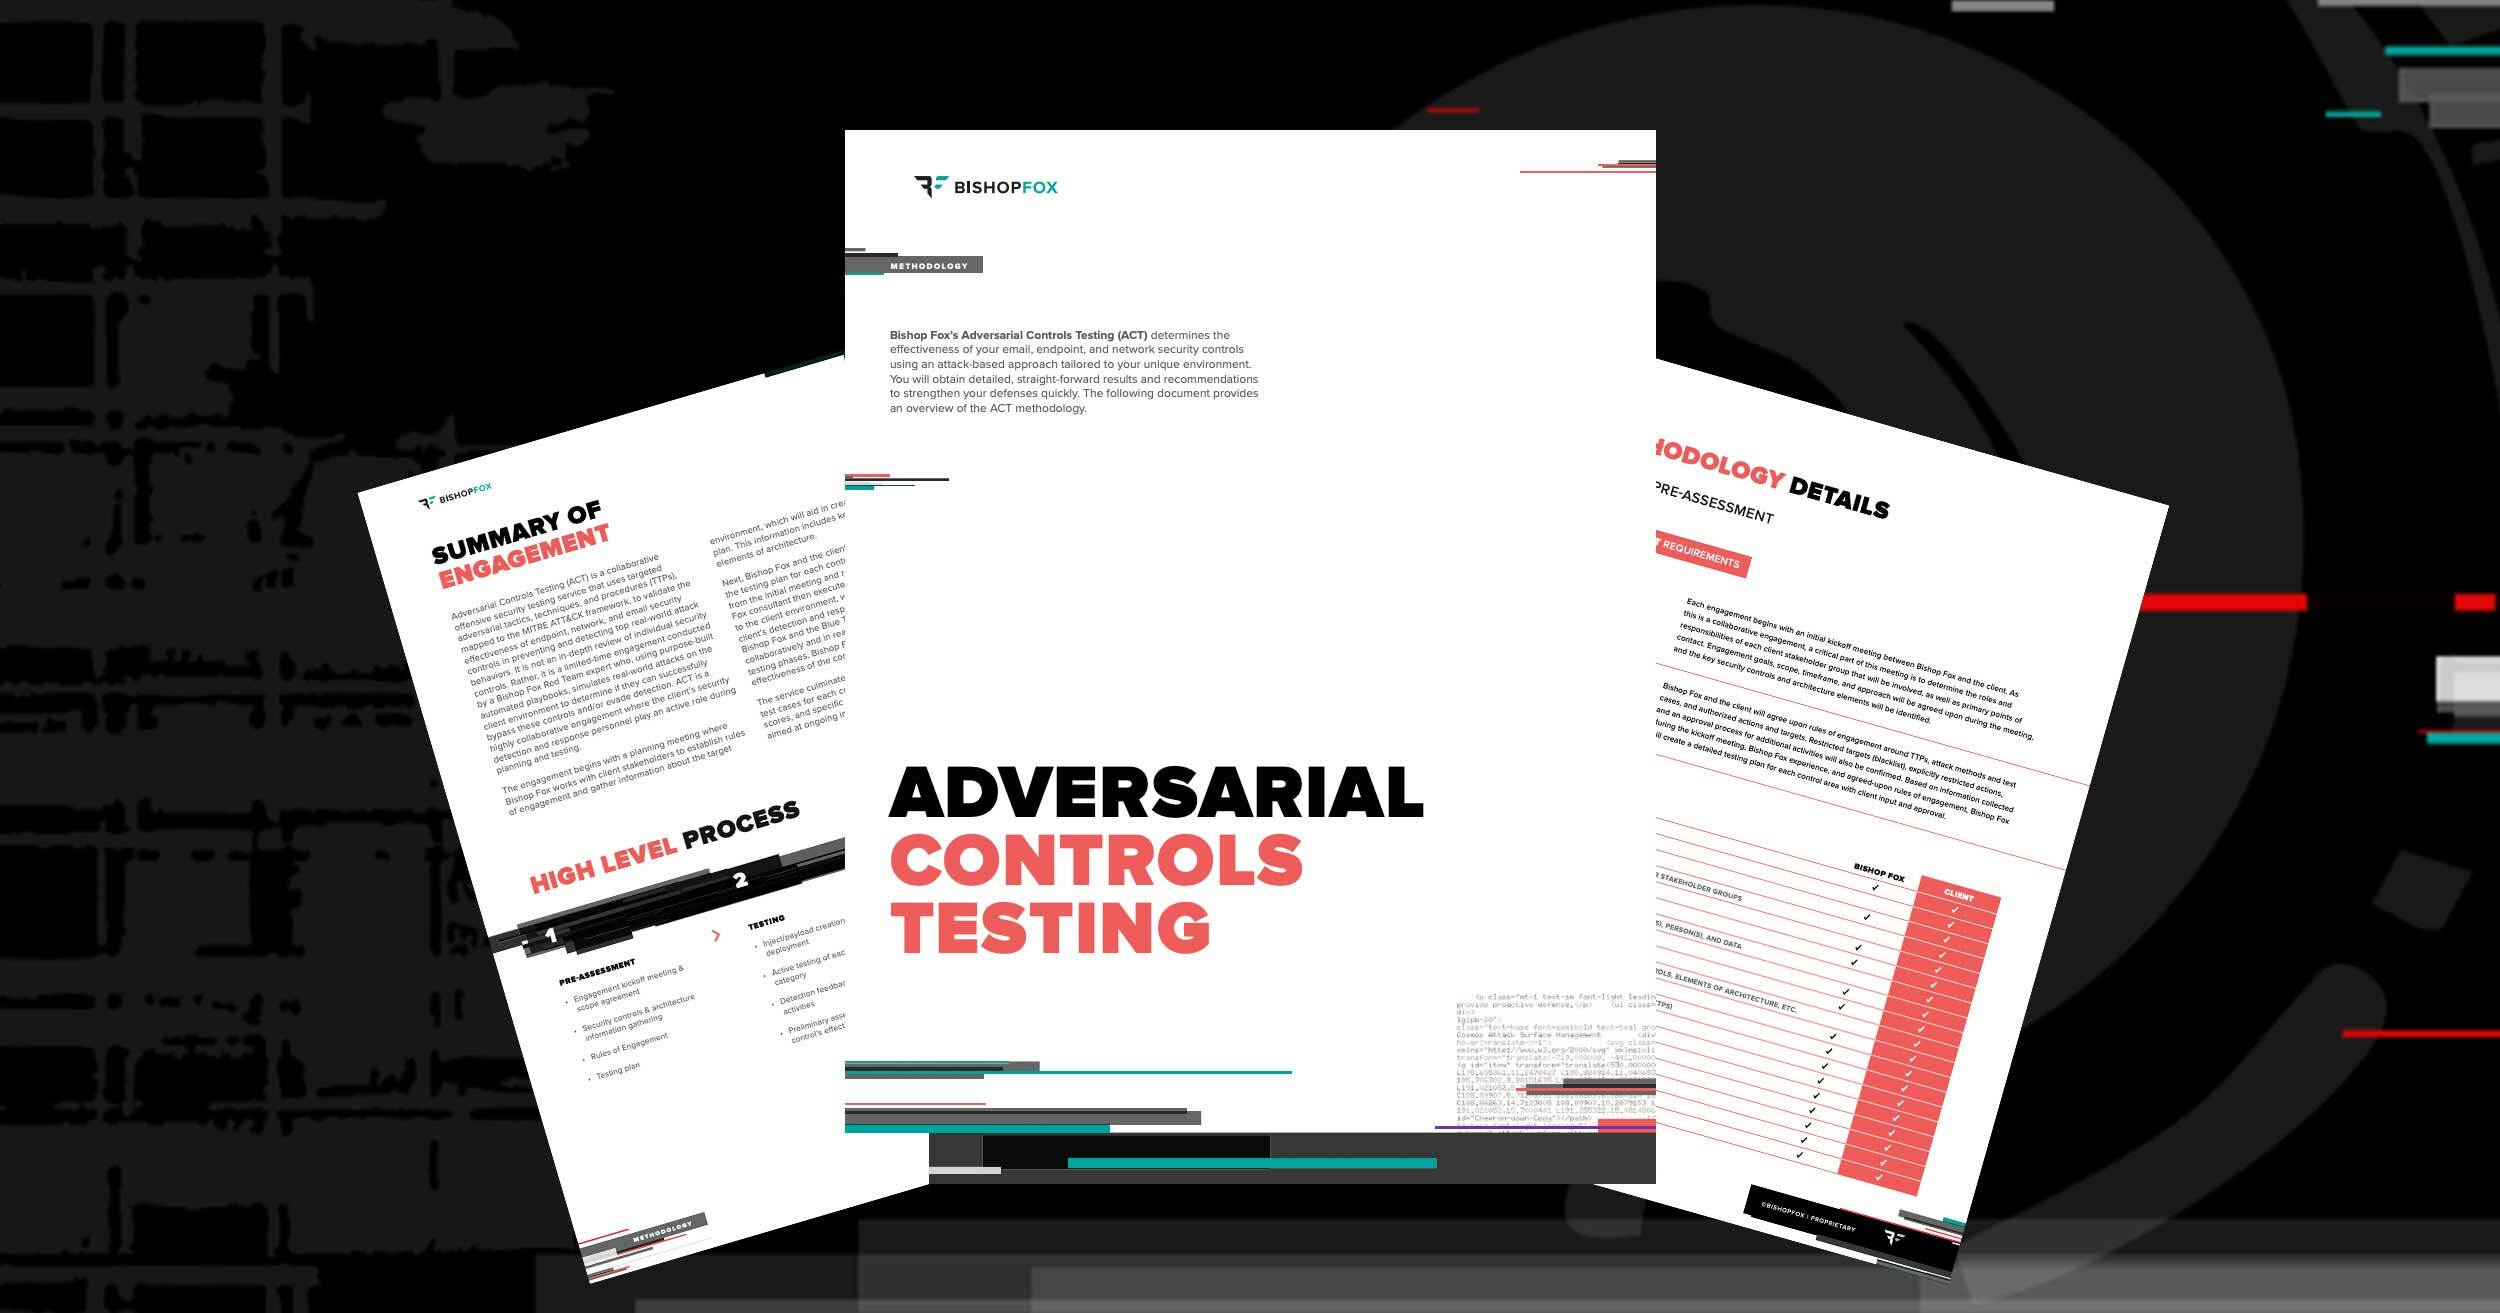
Bishop Fox’s Adversarial Controls Testing (ACT) engagement determines the effectiveness of your email/phishing, endpoint, and network security controls using an adversarial, attack-based approach mapped to the MITRE ATT&CK framework. These collaborative engagements include testing plans tailored to your unique environment, executed by Bishop Fox Red Team experts leveraging purpose-built automated playbooks.
Standard engagements take three weeks or less to complete, upon which time you receive detailed, straight-forward results and recommendations to strengthen your defenses.
This detailed methodology guide covers:
- The complete ACT engagement process from kickoff to final reporting
- Pre-assessment planning and rules of engagement
- Active testing approach using MITRE ATT&CK-mapped TTPs
- How Bishop Fox and your Blue Team collaborate in real-time
- Example test cases for email, endpoint, and network controls
- Scoring methodology and assessment criteria
- Delineation of responsibilities between Bishop Fox and client teams
- Reporting structure and recommendations for control improvement
WHY ADVERSARIAL CONTROLS TESTING?
Traditional security assessments often focus on finding vulnerabilities in applications or infrastructure. ACT takes a different approach—testing whether your defensive security controls can actually stop real attacks.
Key benefits:
- Validate control effectiveness against real-world adversary behavior
- Identify gaps in prevention and detection capabilities
- Receive actionable recommendations to strengthen defenses
- Collaborate with Bishop Fox experts in real-time during testing
- Gain visibility into which attacks your controls block, partially block, or miss entirely
WHO SHOULD READ THIS METHODOLOGY:
- CISOs and security leaders evaluating offensive security testing approaches
- SOC managers and Blue Team leads responsible for detection and response
- Security architects designing defensive controls
- Compliance and risk teams validating control effectiveness
- Organizations preparing for adversarial controls testing engagements
Get detailed insights into how Bishop Fox conducts Adversarial Controls Testing engagements. This comprehensive methodology document outlines the step-by-step process, collaboration model, example test cases, and delineation of responsibilities critical to validating your security controls.